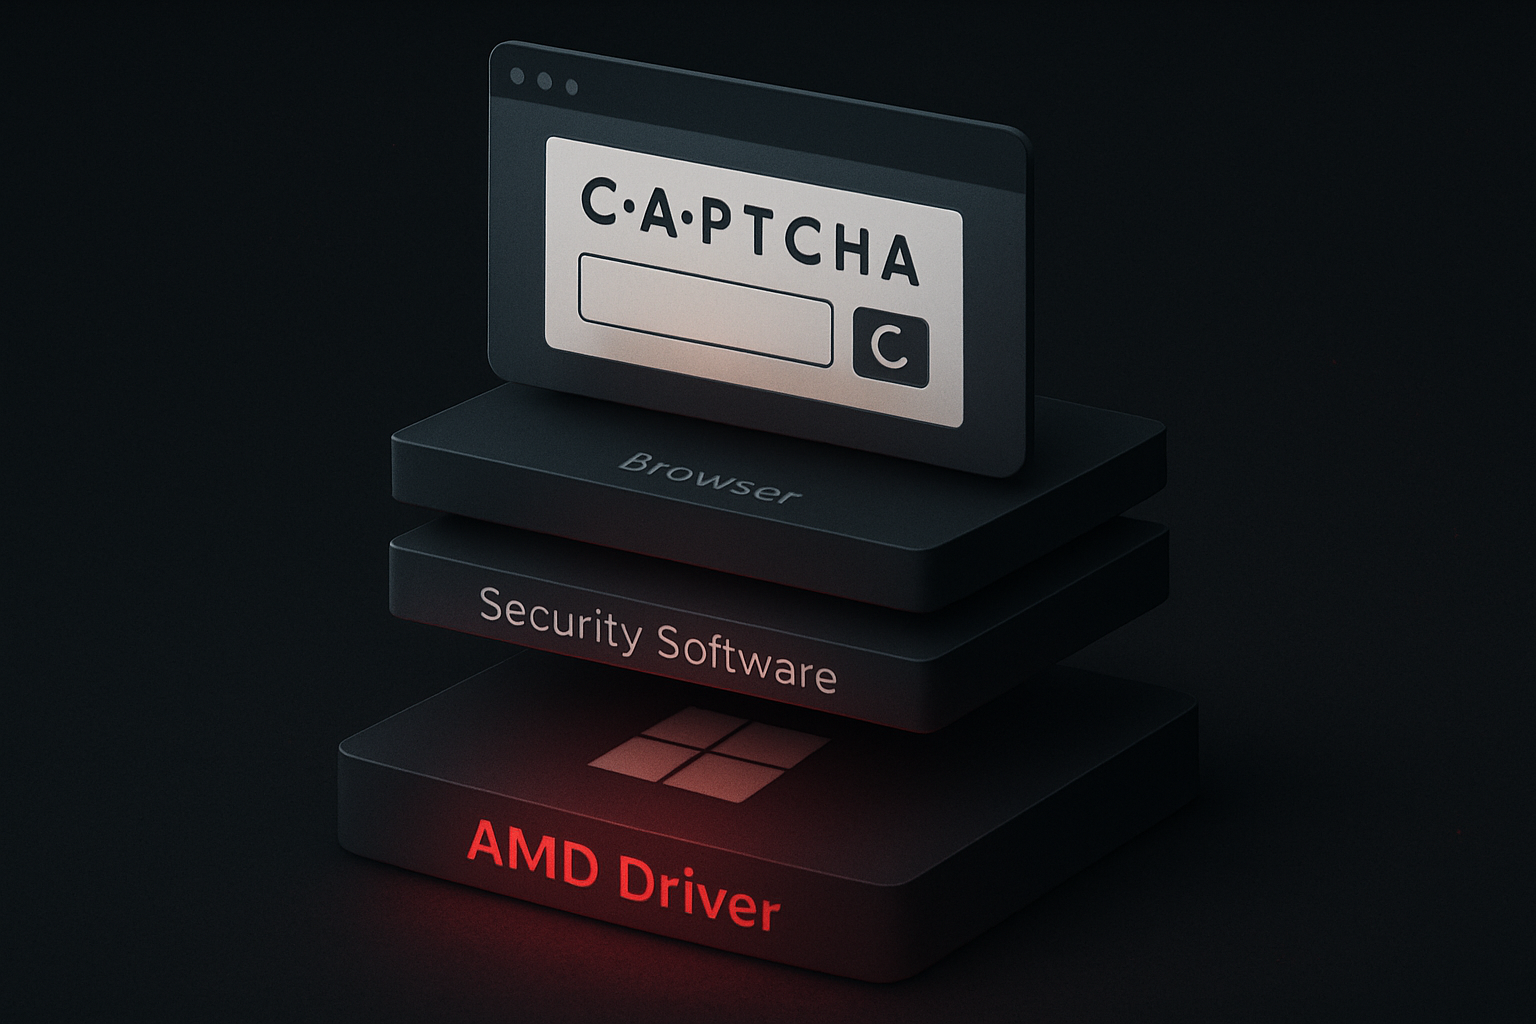
Legitimate device drivers, signed by hardware manufacturers and trusted by operating systems, are rarely thought of as attack vectors. Yet researchers tracking the Lunex stealer malware have documented a sophisticated abuse of AMD drivers to disable endpoint security controls—a technique that sidesteps many conventional detection mechanisms and represents a shift in how malware operators approach post-compromise activity.
The Four-Stage Attack Chain
The Lunex operation, documented by researchers at Ontinue, begins with deceptively simple social engineering. Targets—primarily Ukrainian-speaking users—encounter fake CAPTCHA verification pages hosted on compromised websites. These pages mimic legitimate Cloudflare challenges, a tactic known as ClickFix. The user clicks through, believing they are completing a security check, but instead downloads an initial payload.
From there, the attack unfolds in stages. The dropper executes, establishes persistence, and prepares the system for credential harvesting. What makes this particular variant noteworthy is the intermediate step: disabling or blinding endpoint detection and response (EDR) solutions before the actual stealer runs. This is where the AMD driver abuse comes in.
Driver Abuse as a Security Bypass
Exploiting legitimate, signed drivers to disable security tools is not new, but it remains effective because kernel-level access is required to remove or silence EDR agents. By leveraging a legitimate AMD driver, Lunex operators gain that access while appearing as trusted system code. The driver itself is not malicious; it is the misuse of its privileged execution context that matters.
This technique, sometimes called "bring your own driver" (BYOD), is particularly difficult to defend against. Traditional signature-based detection flags known malicious binaries. A signed AMD driver, however, passes initial scrutiny. Behaviour-based detection must then identify suspicious driver calls or unusual sequences of kernel operations—a higher bar than catching a known piece of malware.
Once EDR is disabled or blinded, the stealer payload runs with reduced visibility. It targets browser credential stores, email clients, and other sensitive data repositories. Users may have endpoint protection installed, yet it remains unaware of the theft occurring beneath it.
The Wider Lunex Malware-as-a-Service Ecosystem
Lunex itself functions as a malware-as-a-service (MaaS) platform, meaning multiple threat actors rent access to the infrastructure, dropper payloads, and distribution mechanisms. This model has become standard in the cybercriminal economy. Rather than developing everything from scratch, operators purchase or lease a turnkey attack platform and customise it for their targets.
The use of compromised Ukrainian websites as distribution points reflects common targeting patterns in Eastern European cybercrime. Attackers compromise legitimate sites, inject malicious content, and serve it to geographically relevant audiences. The fake CAPTCHA pages add a social engineering layer that increases the likelihood of user interaction.
Implications for Infrastructure and Security Teams
For hosting providers, system administrators, and security operations centres, this activity underscores several operational realities. First, endpoint security alone is insufficient if it relies on user-mode agents that can be disabled by kernel-level exploits. Layered detection—network monitoring, process behaviour analysis, and threat intelligence sharing—becomes essential.
Second, credential theft remains a primary attack objective. Even after an initial compromise, attackers spend time harvesting credentials before moving to lateral movement or persistence. Monitoring for unusual authentication patterns, enforcing strong multi-factor authentication, and using secrets management tools can mitigate the impact of compromised passwords.
Third, supply chain trust—in this case, trust in signed drivers—requires continuous reassessment. Organisations should maintain inventories of legitimate drivers in use, monitor for abnormal driver loading behaviour, and stay informed about driver vulnerabilities that could be weaponised in this way.
The Lunex campaign demonstrates that sophisticated attackers do not need zero-day exploits or custom malware to be effective. Combining social engineering, MaaS infrastructure, and legitimate-but-exploitable system components creates a resilient attack that traditional defences often miss. Defending against it requires understanding the full chain of compromise, not just the final malware payload.

